Asos Confirms Customer Data Breach After Rogue App Alert
2 min read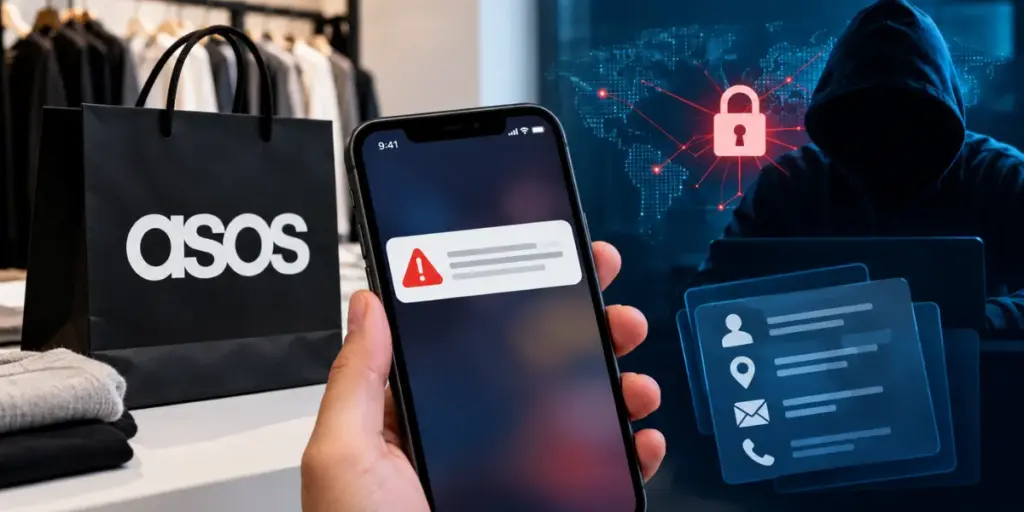
UK fashion retailer Asos has confirmed that hackers accessed customers’ personal information after using the company’s own app notification system to warn users that Asos had been compromised.
The company disclosed the incident in a filing with the London Stock Exchange, saying attackers gained access to a third-party platform that hosts data Asos uses to communicate with its customers.
According to Asos, the stolen information includes customer names and contact details. BBC News reports that the compromised data also includes home addresses, phone numbers and email addresses. Some customer profile notes were reportedly exposed as well, including information about users’ website search queries.
The incident became public after hackers managed to send an unauthorised notification through Asos’ customer communication system. The message was shared by a number of users on social media.
The notification was directed at Asos’ data protection officer and IT department. In it, the hackers claimed they had “fully compromised” company data hosted on Snowflake and warned the retailer that the information could be released publicly unless Asos engaged with them.
The message said: “Engage with us, or we will leak it.”
Rather than simply contacting Asos privately, the attackers appear to have used the company’s own notification channel to put pressure on the retailer. By reaching customers directly through the app, the hackers were able to make their claims public and increase the pressure on the company.
According to Bleeping Computer, the attackers reportedly gained access to the Snowflake environment by impersonating a trusted contact in an attempt to obtain login credentials. Snowflake, however, has said that its systems themselves were not breached.
Several details about the attack remain unclear. It is not known whether the Snowflake environment operated by Asos had multi-factor authentication enabled. There is also no confirmed explanation for how the attackers obtained access to the system used to send Asos’ in-app push notifications, a function that is frequently managed through a third-party service.
The group behind the attack identifies itself as Xuanye Group. So far, the hackers have not said how much data they claim to have obtained.
The scale of the potential incident could be significant. Asos says on its website that it has 17 million customers, although it has not been stated that all of those customers were affected by the breach.
The incident also follows a similar attack involving fintech company Betterment earlier this year. In that case, hackers gained access to a third-party marketing platform and used it to impersonate the company, sending customers a cryptocurrency scam. The attackers also obtained customer information including names, email addresses and phone numbers.
The Asos incident highlights how attackers can exploit third-party platforms and communication tools to reach customers directly, even when the company itself may not be the direct target of an underlying platform breach.
Also read : Tab Emerges With $300M Valuation as AI Assistant Race Grows